01 / The problem
Context
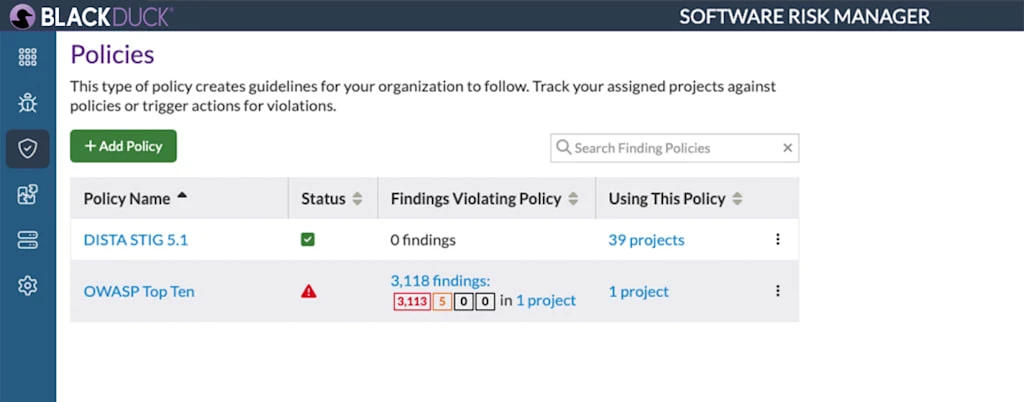
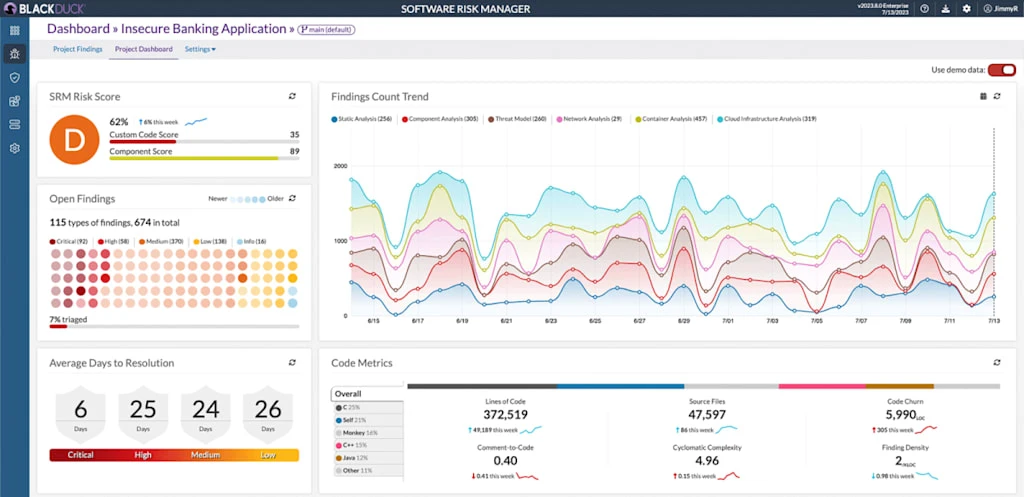
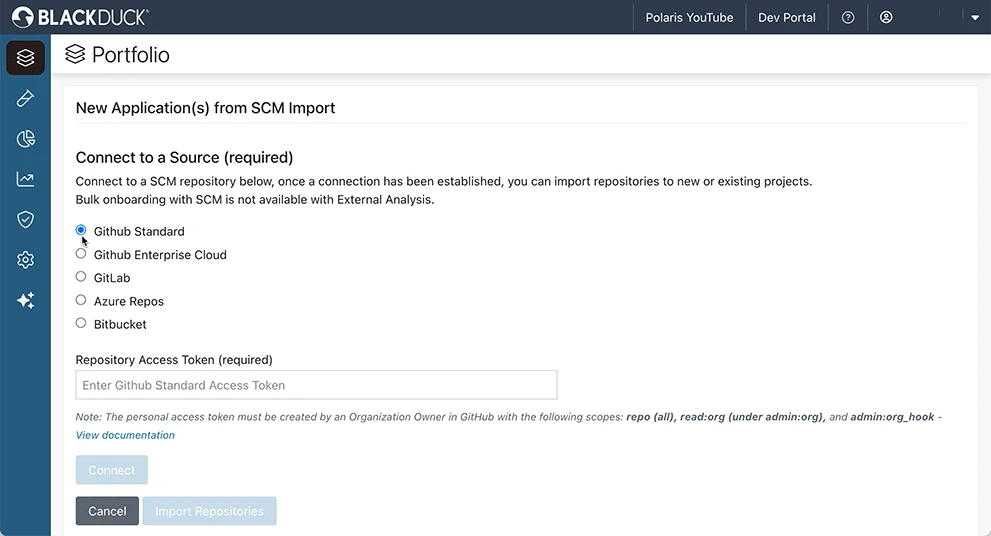
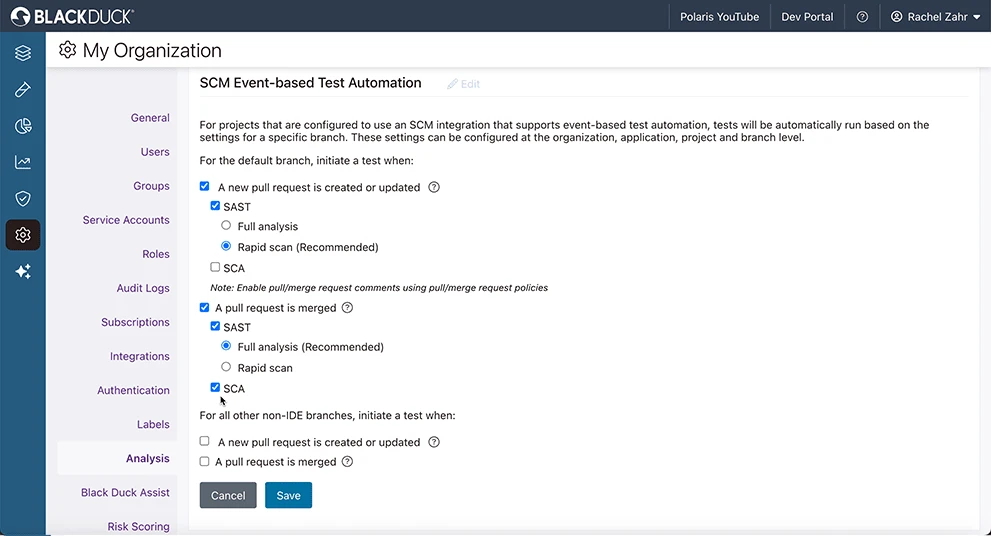
Black Duck addresses a connected operational workflow: application security testing and software composition analysis. Teams using this type of platform need consistent context as information moves between systems and people.
02 / The experience
A connected product workflow
This product study focuses on the path from inspect code to verify remediation. The central interface challenge is making the next action understandable while preserving the state and evidence behind it.
- 01Inspect code
- 02Analyze components
- 03Prioritize finding
- 04Verify remediation
03 / Technical perspective
Engineering approach
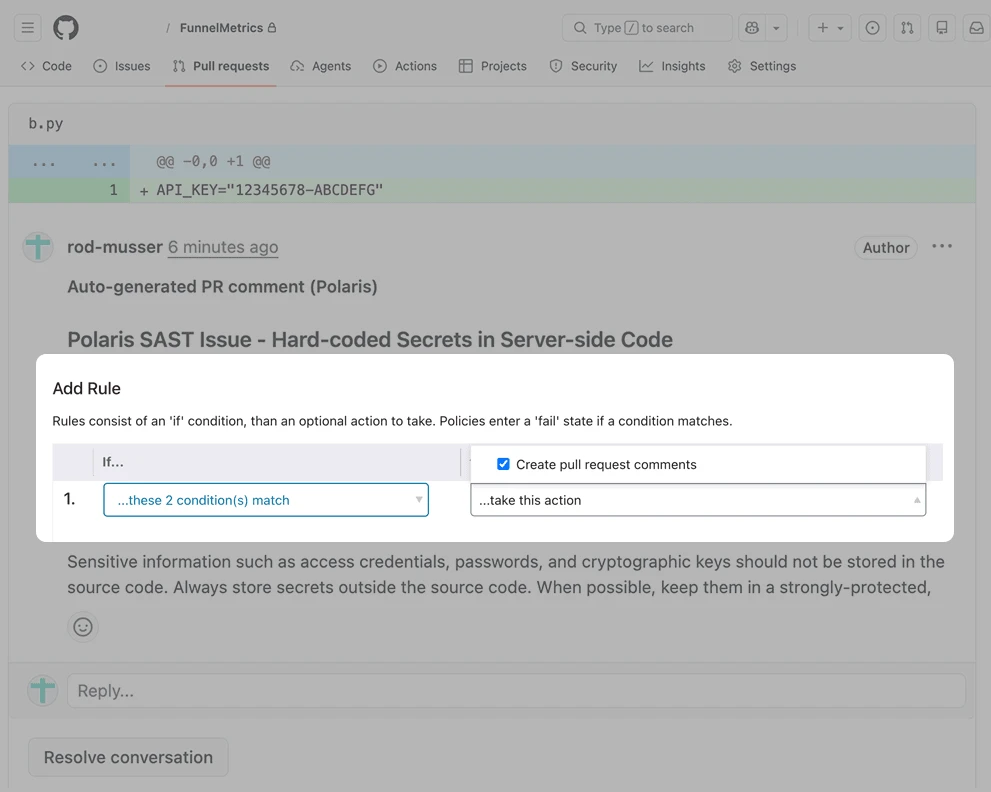
A proposed security pipeline should connect a finding to a specific build and component version. Separate raw scanner output from triaged, actionable issues to reduce alert fatigue.
This section outlines a proposed approach, rather than the company’s verified internal implementation.
04 / Reliability
Testing priorities
Check false positives, transitive dependencies, suppressed findings, and rescans after remediation. Preserve evidence explaining why a finding was accepted or dismissed.
05 / Source & attribution
Explore the product
This independent study is based on the company’s public website. The gallery contains imagery sourced from the company’s official website and public product resources. Images belong to their respective owners. This study does not claim a personal role in building the product.
Visit Black Duck ↗